A security incident has emerged on underground cybercrime forums, where a threat actor operating under the alias TheHatman claims to have obtained data associated with the Microsoft Azure environments of nine multinational organizations, most prominently quick-service restaurant giant McDonald’s, retail leader Gap Inc., and telecommunications provider Vodafone. The adversary is actively advertising the sale of sensitive employee records and tenant account data allegedly exfiltrated using compromised Azure credentials. Observed forum activity tied to this listing spans from August 1, 2026 through August 12, 2026, the most recent date on which related postings were identified.
These claims have not been independently verified, and Gap Inc. has publicly disputed them (see the ThreatMon Assessment section below).
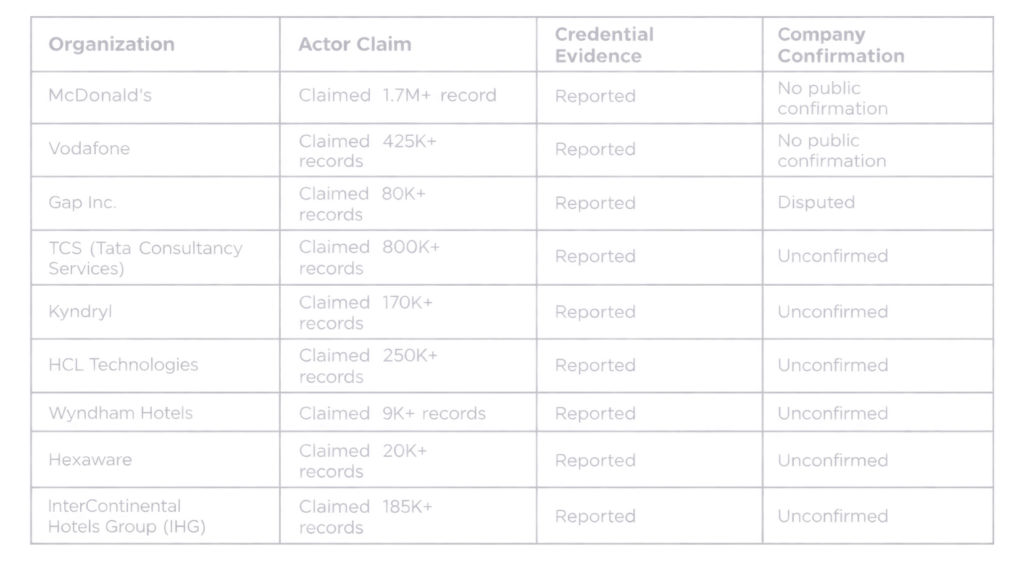
According to claims posted by the TheHatman threat actor, the alleged breach impacted distinct business units across nine entities spanning the QSR, retail, telecommunications, IT services, and hospitality sectors, with the following volumes of exposed corporate information claimed by the actor:
If validated, this incident would represent a serious Azure identity compromise affecting global leaders across multiple sectors. At this stage, however, the claims rest on forum postings and infostealer-derived credential evidence rather than confirmed tenant intrusions.
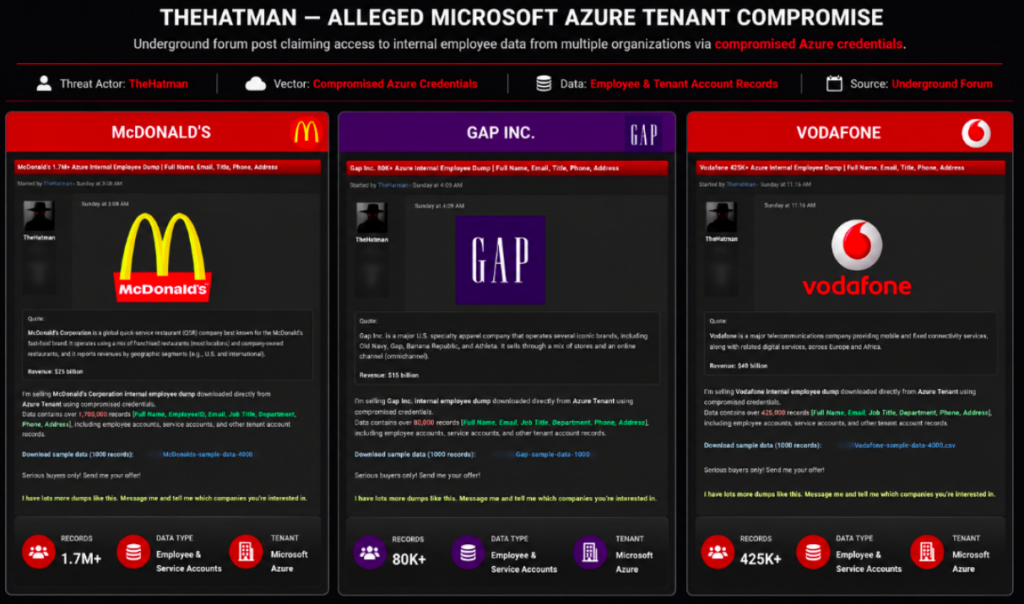
Summary of TheHatman’s alleged Azure-related data claims involving McDonald’s, Gap Inc., Vodafone, and TCS (Tata Consultancy Services), including the claimed record volumes and reported data types. The information presented is based on underground forum claims and available infostealer evidence and should not be interpreted as confirmation of successful Azure tenant compromise.
The datasets allegedly offered for sale on underground markets are claimed to contain both individual user attributes and operational system details. The scope of the claimed employee data exposure encompasses:
The inclusion of service accounts alongside standard employee accounts, if accurate, would elevate the operational risk significantly. Service accounts in Azure often hold elevated permissions to execute automated scripts, access databases, or interface with third-party applications. If an adversary did obtain active credentials for service accounts, the potential for lateral movement and persistence within the enterprise cloud infrastructure would increase substantially.
The claims made by TheHatman center around alleged unauthorized access to corporate Microsoft Azure environments using valid, yet reportedly stolen, access keys or user credentials. In enterprise cloud deployments, an Azure tenant compromise typically occurs when threat actors leverage initial access vectors such as compromised corporate credentials harvested via infostealers, phishing campaigns, or credential stuffing to bypass traditional boundary defenses.
In this case, the specific initial access vector has not been confirmed. The infostealer intelligence underpinning this reporting characterizes the vector as inconclusive: infostealer malware, stolen session tokens, weak or absent MFA, and over-privileged third-party integrations are all plausible explanations, but none has been established as the confirmed cause.
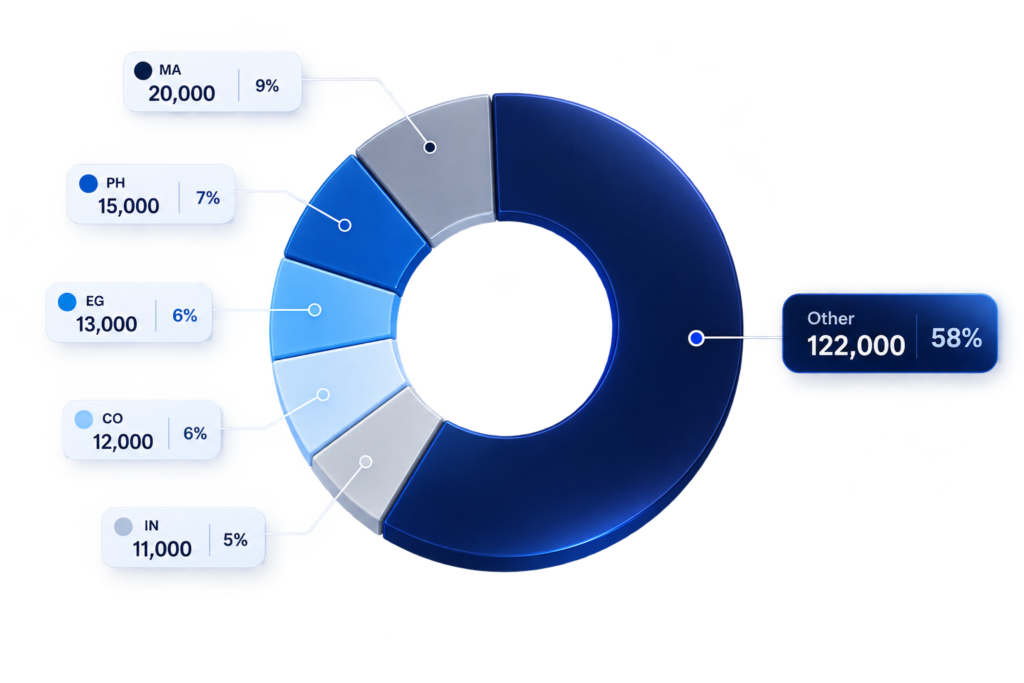
The country distribution of windowsazure.com infostealer leaks observed during 2025–2026 highlights the geographic concentration of compromised credentials and provides an indication of the potential exposure across affected regions. Countries with higher leak volumes may represent a greater potential threat to organizations operating in those regions, particularly where compromised corporate credentials could enable account takeover, Business Email Compromise (BEC), unauthorized cloud access, or further intrusion activity.
Claim that a potential data-stealing program related to Microsoft Azure has been discovered worldwide.
Claims that a potential data theft scheme linked to Microsoft Azure has been uncovered worldwide: The evidence examined shows that Microsoft credentials associated with Gap Inc.’s corporate account appeared in the logs of the data theft scheme. Gap Inc. denies that this constitutes a security breach; in its investigation, the company stated that it found no evidence of unauthorized access and that the relevant data was outdated and not considered sensitive.

Allegation of a Possible Microsoft Azure InfoStealer Discovery Regarding Gap Inc.
Tata Consultancy Services (TCS) is also named among the organizations referenced in the actor’s claims. Available infostealer log data contains multiple entries associated with TCS-related Microsoft/Azure services, with records exposing usernames, passwords, IP addresses, geographic information, log dates, and employee status. These findings indicate the presence of credentials associated with TCS-related services in infostealer logs, but do not independently confirm that the credentials were used to access TCS’s Azure environment.
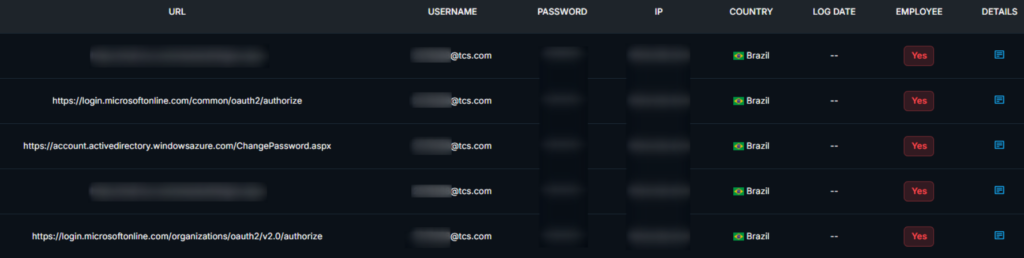
Allegation of a Possible Microsoft Azure InfoStealer Discovery Regarding TCS(Tata Consultancy Services)
Kyndryl is also named among the organizations referenced in the actor’s claims, with multiple Kyndryl-related Microsoft service credentials observed in infostealer logs, including associated usernames, passwords, IP addresses, geographic information, and log dates. The findings confirm the presence of Kyndryl-related credentials in infostealer logs but do not independently establish unauthorized access to its Azure environment.
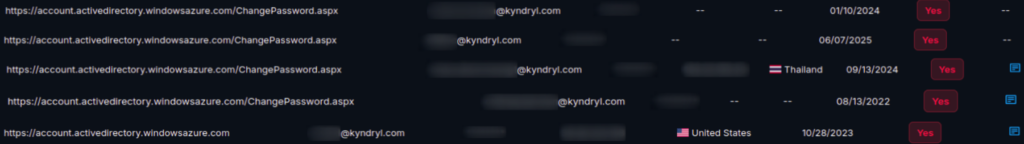
Allegation of a Possible Microsoft Azure InfoStealer Discovery Regarding Kyndryl.
HCL Technologies is also named among the organizations referenced in the broader campaign. Available infostealer log data contains entries associated with HCL Technologies-related Microsoft services, including usernames, passwords, IP addresses, country information, and log dates. These records indicate that credentials associated with HCL Technologies’ corporate services appeared in infostealer logs, but do not independently confirm that the credentials were used to access the company’s Azure environment.

Allegation of a Possible Microsoft Azure InfoStealer Discovery Regarding HCL Technologies.

Allegation of a Possible Microsoft Azure InfoStealer Discovery Regarding Gap Inc.
The table below summarizes the current status of each named organization based on actor claims, available credential evidence, and public company confirmation as of this writing:
The potential distribution of this claimed data poses multifaceted theoretical threats to the named organizations, as well as their supply chain partners, assuming the underlying claims are substantiated. Even in scenarios where core databases remain uncompromised, the exposure of corporate identity structures could provide bad actors with blueprints for follow-on cyberattacks.
Business Email Compromise (BEC) and Spear Phishing
With access to names, job titles, internal departments, and email addresses, threat actors could construct convincing BEC campaigns, impersonating executives, HR representatives, or IT administrators using detailed internal organizational structures to trick employees into transferring funds or revealing additional administrative credentials.
Corporate Account Takeover
The exposure of service accounts and compromised business email credentials, if genuine, would create pathways for corporate account takeover. When threat actors acquire authentic login details combined with contextual organizational data, they can bypass basic authentication hurdles, establish persistent access, and compromise downstream enterprise software solutions integrated into the Azure tenant ecosystem.
Supply Chain and Reputation Risks
Operating in critical sectors like retail, telecommunications, IT services, hospitality, and quick-service dining means that trust is paramount. An alleged data exposure involving internal operational details, even unconfirmed, can lead to regulatory scrutiny, contractual questions from enterprise partners, and reputational pressure across global consumer and client bases.
Organizations seeking to determine whether they are affected by this or similar campaigns should focus on the following detection steps:
To counter threats posed by actors like TheHatman and mitigate the risk of an Azure tenant compromise, security leaders must enforce rigorous cloud identity governance and zero-trust operational architectures. Organizations relying on cloud environments should implement the following defensive actions:
Campaigns like TheHatman’s underscore why continuous, credential-focused visibility matters as much as perimeter defense. ThreatMon’s infostealer intelligence and dark web monitoring capabilities are built to surface exactly this type of exposure early correlating leaked credentials with corporate domains and Microsoft/Azure-linked services, tracking underground forum listings as they emerge, and flagging service account exposure before it can be leveraged for lateral movement.
By combining infostealer log analysis with ongoing monitoring of cybercrime forums and marketplaces, ThreatMon enables security teams to identify compromised credentials tied to their organization, assess the credibility and scope of actor claims like TheHatman’s, and prioritize remediation, such as credential resets and session invalidation, before unverified exposure has a chance to translate into confirmed compromise.
The claims made by the TheHatman threat actor regarding alleged Microsoft Azure-linked data exposure affecting McDonald’s, Gap Inc., Vodafone, and six additional organizations highlight the critical importance of cloud identity security, regardless of whether every claim is ultimately substantiated. Gap Inc.’s public denial and the inconclusive attack-vector assessment are important context that should accompany any reporting on this campaign as organizations continue to migrate operational workflows to multi-tenant cloud ecosystems, where identity has effectively become the new security perimeter.
Protecting against high-profile claims of employee data exposure and account takeover requires continuous vigilance, strict access management, and proactive threat hunting. Cybersecurity professionals and decision-makers must treat cloud credential hygiene as a top strategic priority to defend their enterprise infrastructures against sophisticated threat actors targeting cloud identities, while also applying appropriate scrutiny to unverified breach claims before treating them as confirmed incidents.

More posts
Share this article
Found it interesting? Don’t hesitate to share it to wow your friends or colleagues
Subscribe to our blog newsletter to follow the latest posts